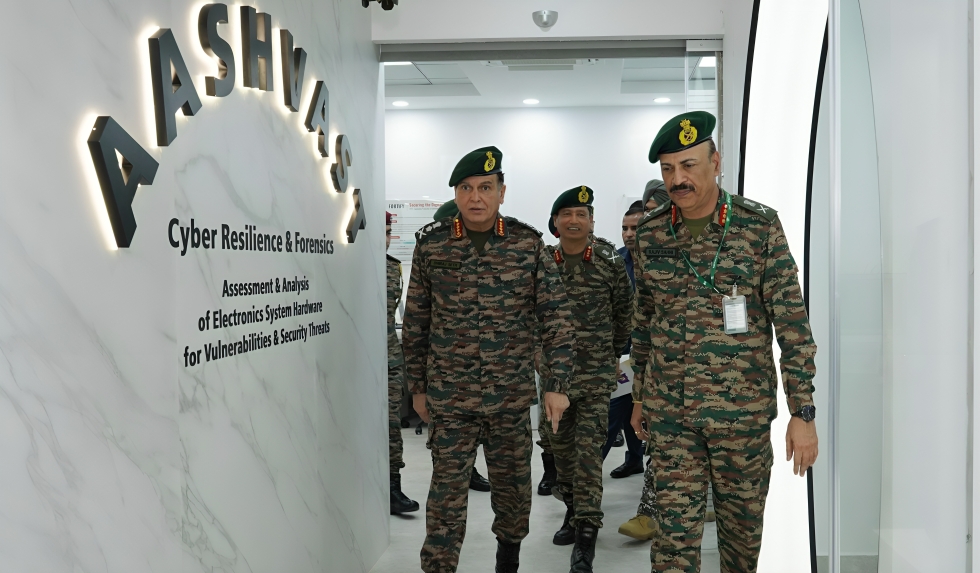

The Indian Army has opened a dedicated facility to inspect military drones for security vulnerabilities, malicious modifications, and Chinese-made components.
Based in New Delhi, the Assessment and Analysis of Electronic Systems Hardware for Vulnerabilities and Security Threats (AASHVAST) facility examines each drone to verify its authenticity and determine whether it has been tampered with.
It scans for hidden passwords, encryption keys, secret command paths, and remote-access tools that hostile actors could exploit.
Its scrutiny extends to whether drones accept only manufacturer-approved software updates and how their security controls withstand GPS spoofing and jamming.
AASHVAST operates entirely offline inside an air-gapped facility, preventing sensitive data from being exposed or stolen during testing.
Its read-only architecture allows technicians to examine software directly from a flight controller or camera payload without writing data to or modifying the drone.
Consolidating Security Reports
The facility rates identified vulnerabilities by severity and presents the findings in plain language within a single security report.
This allows the technician examining the drone and the officer responsible for approving it to work from the same document.
Army Chief General Dhiraj Seth inaugurated the facility on August 14.
The army said AASHVAST would strengthen the cyber resilience and operational readiness of critical defense platforms while supporting India’s domestic defense industry.


